This guide explains how “P0rn0” content is handled across platforms, focusing on compliance, verification, and risk controls. Objectively, “P0rn0” is an obfuscated term often used online to discuss pornographic material while attempting to evade moderation filters. The guide outlines safer, policy-aligned approaches, including supplier governance, age-gating requirements, and audit-ready documentation.
When “P0rn0” appears in online discussions, the immediate concern is not sensationalism—it’s governance. From platform moderation to advertiser suitability and legal exposure, organizations should treat adult or pornographic material as a high-risk category. This article provides an objective, industry-style framework for evaluating “P0n0”/“P0rn0” use cases, supplier practices, and operational safeguards, without promoting or distributing explicit content.
It also addresses a common misunderstanding: some teams assume that obfuscation, leetspeak spelling, or partial keyword masking reduces compliance risk. In practice, most mature moderation and risk controls evaluate meaning, context, user intent indicators, and metadata. Obfuscated references therefore frequently increase scrutiny rather than decreasing it. For organizations handling user-generated content, search indexing, marketplaces, content catalogs, creator platforms, ad targeting, or third-party feeds, the correct approach is to classify “P0rn0” as adult-related content for policy purposes and implement controls that are proportionate to that risk.
Throughout this guidance, the focus remains on compliance, safety, and operational resilience. The goal is to help organizations build defensible processes—processes that can withstand audit, regulator questions, partner contract disputes, and incident response reviews—without providing advice that would enable bypassing filters or distributing prohibited material.
“P0rn0” is commonly used as a visual substitution for “porn” to reduce keyword blocking, bypass automated filters, or fit within character-limited contexts. In practical terms, it still points toward adult/pornographic subject matter. That distinction matters: even if the spelling is obfuscated, very moderation systems and compliance teams evaluate content by meaning, context, and metadata—not just exact strings.
In day-to-day moderation work, “P0rn0” often appears in multiple forms:
From an industry perspective, you should assume that “P0rn0” references are treated as adult content. Therefore, organizations that handle user submissions, marketing assets, content catalogs, or third-party feeds should apply the same controls they use for explicit material categories—age gating, restricted distribution, and stricter review workflows.
It is also worth noting a subtle governance issue: even if “P0rn0” is used only as a placeholder (for example, in a sentence discussing “why people use P0rn0 keywords”), the surrounding context may still require special handling. Many platforms treat adult-related “discussion” differently from adult “distribution.” The correct response depends on your classification scheme, your risk appetite, and your legal obligations, but the safe default is to treat “P0rn0” as a high-confidence adult indicator unless review or context analysis suggests otherwise.
Although the exact rules vary by jurisdiction and platform, adult content categories often trigger a bundle of operational obligations. These can include:
In short: using “P0rn0” as a keyword does not neutralize risk. It may, in some contexts, increase risk because it signals intent to evade controls or conceal meaning—something compliance teams take seriously.
To expand on that, many organizations encounter adult-related risk at multiple levels:
Because of these layered risks, governance teams often adopt a “severity-tier” model. “P0rn0” and semantically similar obfuscations are generally treated as at least “adult-related and restricted,” even when the visible text appears ambiguous. That model prevents the system from becoming overly dependent on exact string matching.
Modern moderation typically combines multiple signals: text classification, visual models, contextual cues, and behavioral patterns. Obfuscated strings like “P0rn0” can be detected through normalization, similarity scoring, and semantic understanding. As a result, organizations should not rely on “string tricks” when designing policies, safeguards, or content taxonomies.
From a technical and operational standpoint, obfuscation creates two governance challenges:
In practice, many mature platforms use a hybrid moderation approach:
For risk teams, the lesson is straightforward: treat obfuscated adult references as equivalent to explicit references for policy purposes.
It’s also important to recognize that obfuscation can be a deliberate attempt to evade filters. That intent may influence enforcement severity, such as escalating to human review more quickly or applying stricter rate limits and account-level controls. However, governance teams should be careful not to “over-penalize” harmless usage; therefore, decisions should still be based on evidence and context, not only the presence of the obfuscated token.
From a governance and operations standpoint, effective controls tend to share the same traits: measurable thresholds, documented decisioning, and audit trails. If you operate a platform, marketplace, or content workflow that might encounter adult-related submissions (including those labeled with “P0rn0”), build controls that cover:
This approach is not about moral judgment; it’s about operational resilience and legal defensibility.
To make “good” more concrete, organizations typically define clear actions for each tier. For example, a governance model might look like this (illustrative, not prescriptive):
The key is that “P0rn0” should generally trigger at least Tier B unless a verified reviewer determines a different meaning with high confidence. This prevents inconsistent enforcement and protects against the “obfuscation bypass” issue where the system mistakenly treats the term as safe because it is misspelled.
Audit readiness is equally central. A robust system should answer the questions auditors ask in plain terms:
The prompt includes an instruction to integrate “price information” and “supplier details.” However, no concrete, verified price or supplier identity was provided. In compliance work, speculation can be dangerous—so this article focuses on how organizations should structure price/supplier evaluations for adult-category supply chains in a verifiable way.
Practically, when negotiating with vendors that may provide or distribute adult-related content (even indirectly), you should obtain:
If you do have specific price quotes or named suppliers, the right method is to validate them against contract documentation and any available third-party assurance—rather than inserting unverified figures into public guidance.
Because adult-related risk can be high, vendor pricing should not be treated as a purely commercial variable. It is often tied to compliance deliverables and should reflect real costs associated with age assurance, moderation coverage, takedown response times, dispute handling, and training. Procurement teams can reduce risk by requiring that supplier pricing be mapped to operational obligations. For instance:
Supplier details matter for another reason: accountability. If an incident occurs (e.g., prohibited material distributed through a feed labeled with “P0rn0”), your ability to trace the responsibility depends on contractual clarity. Good supplier governance includes:
Many teams prefer a single end-to-end workflow. Below is an operationally realistic structure for handling “P0rn0” references and related adult categories—again, focused on compliance and risk control rather than explicit material distribution.
These steps align with broader industry practices for content safety: classification, access control, review, and auditable enforcement.
To expand this into a more “operational” view, consider adding these implementation details that often determine whether a workflow actually works under pressure:
Another critical area is “indexing and recommendation controls.” Even if you age-gate content, you must ensure it does not leak into public surfaces that bypass gating—such as search results previews, metadata shown to logged-out users, social share thumbnails, or autocomplete suggestions. “P0rn0” tokens might be used in indexing terms. Good governance therefore treats obfuscated adult terms as sensitive metadata that should be restricted in discovery surfaces.
The following sections are included as a comparison and operational supplement. (No hyperlinks are listed in the table, per instructions.)
| Approach | Top for | Key requirements | What to document |
|---|---|---|---|
| Keyword + semantic moderation | Initial triage of obfuscated adult references such as “P0rn0” | Policy mapping; normalization rules; false-positive handling | Classifier thresholds, review sampling results |
| Human escalation workflow | Borderline or context-dependent cases | Trained reviewers; documented decision criteria | Reviewer guidelines version; adjudication logs |
| Age-gating + restricted access | Adult content that is permitted only for adults | Age assurance; access logs; secure storage policies | Age check evidence; audit trails for access events |
| Supplier governance program | When content/feeds come from third parties | Certifications; right-to-audit; incident reporting SLAs | Vendor attestations; compliance reports; corrective action records |
To strengthen the value of this comparison table, organizations often establish explicit “handoff criteria” between approaches. For example:
This prevents scenarios where obfuscation causes the system to “hedge” incorrectly and treat adult-adjacent content as benign because the exact token was misspelled.
Because “P0rn0” connects to adult content safety and platform governance, it’s useful to anchor decisions to widely recognized guidance on harmful content systems. One reliable reference point is the EU Digital Services Act (DSA), which outlines obligations for online platforms, including risk assessment and content moderation transparency mechanisms (where applicable). In addition, many organizations consult the OECD guidance and national regulators’ materials on online safety, age assurance, and risk-based compliance approaches.
For classification and moderation practices, companies also commonly align with internal risk management standards and, when available, third-party assurance reports. (When you implement controls, always confirm current legal requirements for your operating jurisdictions and your specific content categories.)
Beyond the DSA and OECD materials, many compliance teams also look to operational best practices that are functionally similar across regulatory regimes:
In the context of “P0rn0,” risk assessments should explicitly mention obfuscation as a risk factor. If your policy does not mention obfuscation and relies on exact string matching, your risk assessment may be incomplete. It is more defensible to document how your system normalizes and semantically interprets obfuscated tokens and how you test for bypass attempts.
Organizations also need to consider how their role in the value chain affects obligations. For example, a platform that hosts content may have different obligations than a search engine, an ad network, or a marketplace listing feed. Yet the common element remains: when adult-related content is involved, the governance requirements tend to intensify.
If your organization encounters “P0rn0” references—through user text, search results, metadata, or supplier catalogs—use this decision guide:
Ask: Is “P0rn0” merely a mention in a discussion, or is it attached to explicit adult material? Classification matters because “mentioning” and “hosting” can be treated differently under platform policies and local laws.
For better accuracy, content type detection should not be limited to the presence of “P0rn0.” Consider whether the reference appears in:
If adult content is present and it is permitted only for adults, implement age gating. Require age assurance before display, downloads, or engagement actions.
Access restriction should include both “content access” and “user journey access.” That means controlling not only the primary content page but also ancillary exposures such as:
Age assurance should be implemented consistently across entry points. If some entry points bypass gating, they can undermine the entire control.
Is the content user-generated, an official catalog asset, or a third-party feed? Supplier governance requirements generally increase when content is imported or distributed through partners.
Source channel identification matters because it changes the evidence you should request and the remedial actions you can take:
Adult/pornographic content should fall under stricter enforcement tiers. Obfuscation patterns like “P0rn0” should not reduce enforcement priority.
Severity tiering should be defined by policy, not by ad hoc interpretation. Create explicit mapping rules, such as:
Even if you allow certain discussion contexts, ensure you do not allow “P0rn0” tokens to act as a functional key that unlocks restricted content discovery without age-gating.
Keep audit-ready records: policy version, decision rationale, escalation pathway, and any user appeal outcomes (if your policy includes appeals).
Good logs should include:
Where suppliers provide adult-category content or metadata, request documented compliance mechanisms, training evidence, and incident response SLAs. Confirm you can exercise contractual remedies if violations occur.
Verification should include both documentation and practical assurance:
Run periodic audits. Measure moderation accuracy using a controlled dataset and track drift over time (new obfuscation strings, new content patterns).
Continuous improvement also includes operational learning:
In very governance systems, yes. “P0rn0” is typically an obfuscated form used to refer to adult/pornographic material. Moderation usually relies on semantic understanding and context, not exact spelling.
Brands should follow their content safety policy: classify the context, remove or restrict content that violates rules, and log actions. If the content includes explicit material or age-inappropriate exposure, escalate to human review and tighten access controls.
Additionally, brand owners should consider whether the appearance is an isolated incident or part of a coordinated pattern (e.g., multiple posts, recurring creators, or a campaign with consistent redirect behavior). Pattern detection can inform enforcement severity and help prevent repeat incidents.
Third-party suppliers can introduce compliance risk through their catalogs, feeds, or moderation coverage. A supplier governance program should include certifications, audit rights, incident reporting SLAs, and corrective action requirements.
Supplier governance also intersects with operational reliability. For example, if a supplier has delayed takedown procedures, your organization might temporarily suspend the feed even if the supplier later claims compliance. Governance teams should be prepared for these scenarios by defining “stop conditions” and contingency plans in contracts.
Yes, obligations can vary by jurisdiction and by whether you are hosting, distributing, advertising, or merely moderating content. Many regions emphasize age assurance, safety risk assessments, and takedown processes. Consult qualified legal counsel for your specific scenario.
As part of compliance maturity, organizations often document how each obligation applies to each role they play. For instance, a platform’s obligations for hosting might differ from those for ad monetization. Yet “P0rn0”-related risk often crosses roles (content labeling, indexing, user account management, advertising). Cross-functional coordination is therefore essential.
Automation is useful for triage, but high-risk categories often require human escalation for uncertain or borderline cases. A hybrid model improves accuracy and provides better auditability.
A key governance principle is that automation should be constrained and measured. That means setting thresholds, monitoring model performance, and ensuring that decisioning is consistent enough to defend during audits. Human review is not just for quality; it is also for accountability where automated confidence is insufficient.
Use verifiable contract documentation and cost models. Don’t publish or rely on speculative figures. Instead, ensure pricing is tied to compliance deliverables—moderation coverage, age gating implementation, takedown support, reporting, and audit capability.
In procurement practice, “cheaper” does not automatically mean “riskier,” but unusually low pricing for adult-category compliance can be a red flag. Governance teams should ask for transparency in what the vendor is actually doing (staffing, technology, review times, escalation processes). The goal is to connect cost to measurable obligations.
Typically not. Obfuscation is often detected through normalization and semantic similarity. Treat obfuscated adult references as high-risk signals for compliance purposes.
Because obfuscation attempts can evolve, governance teams should continuously monitor for new variants. Over time, maintaining a dynamic taxonomy and regularly updating detection rules is often more effective than attempting to list every possible string.
To make this actionable, here are expert-oriented recommendations that organizations commonly adopt:
Below are additional operational practices that can help teams implement these recommendations without creating blind spots:
For moderation quality, teams often track metrics such as:
These metrics provide operational feedback loops. They are more defensible than subjective claims because they demonstrate that the organization is measuring and improving its system.
“P0rn0” is top understood as an obfuscated pointer to adult content, and governance teams should treat it accordingly. The responsible path is not to experiment with bypass tactics, but to strengthen classification, age-restricted access controls, human escalation, and supplier governance. When these elements are documented and consistently applied, organizations reduce legal exposure and protect users—while building operational trust in how safety decisions are made.
Ultimately, compliance is an operational capability. Treating obfuscated adult references as high-risk is part of building that capability: it aligns policy interpretation with how modern moderation works, it supports auditability, and it reduces the chance that minor misunderstandings or technical bypasses lead to major harm. Organizations that invest in robust detection, clear enforcement tiers, strong logging, and supplier accountability are better positioned to handle “P0rn0” and similar obfuscation patterns responsibly, consistently, and defensibly.
A Guide to Cost-Efficient Small Electric Cars for Seniors
Mastering Debt Consolidation: Boost Your Credit Score and Manage Interest Rates
Your Guide to Loans, Credit Checks, and Interest Rates
Affordable Independent Living: Finding the Right Senior Housing
Guide to Senior Living Apartments: Affordable and Comfortable Environments
Leasing a Car: Expert Tips for Your Next Vehicle
Maintaining Oral Health After Tooth Loss with Dental Implants
Maintaining Oral Health with Dental Implants for the Elderly
Understanding 1333 Supplier Requirements and Pricing Factors
Understanding 692423217 53: Supply, Pricing, and Sources
This guide explains how to evaluate 692423217 53 within supplier and pricing workflows, focusing on documentation, sourcing risk, and compatibility checks. Background context covers what such product identifiers typically represent in procurement, why supplier details matter for traceability, and how to interpret price signals without assumptions. The guide then provides objective steps and requirements for comparing options.
Lino Pimentel: How to Evaluate Quality and Value
Lino Pimentel is often referenced in discussions about sourcing, credibility, and practical decision-making. This guide offers objective background on the name’s role in marketplace conversations and outlines an expert framework for evaluating quality, supplier fit, and consistent value—using clear conditions, trade-offs, and due-diligence steps you can apply before committing.
Understanding “P0rn0” and Content-Compliance Risks
This guide explains how “P0rn0” content is handled across platforms, focusing on compliance, verification, and risk controls. Objectively, “P0rn0” is an obfuscated term often used online to discuss pornographic material while attempting to evade moderation filters. The guide outlines safer, policy-aligned approaches, including supplier governance, age-gating requirements, and audit-ready documentation.
Colbate Supply and Quality Guide for Buyers
This guide explains how to source Colbate reliably, what quality signals to check, and how to evaluate suppliers with consistent purchasing conditions. It provides an objective background on what “Colbate” typically refers to in procurement contexts, and focuses on practical due diligence: documentation, material consistency, handling, and inspection workflows.
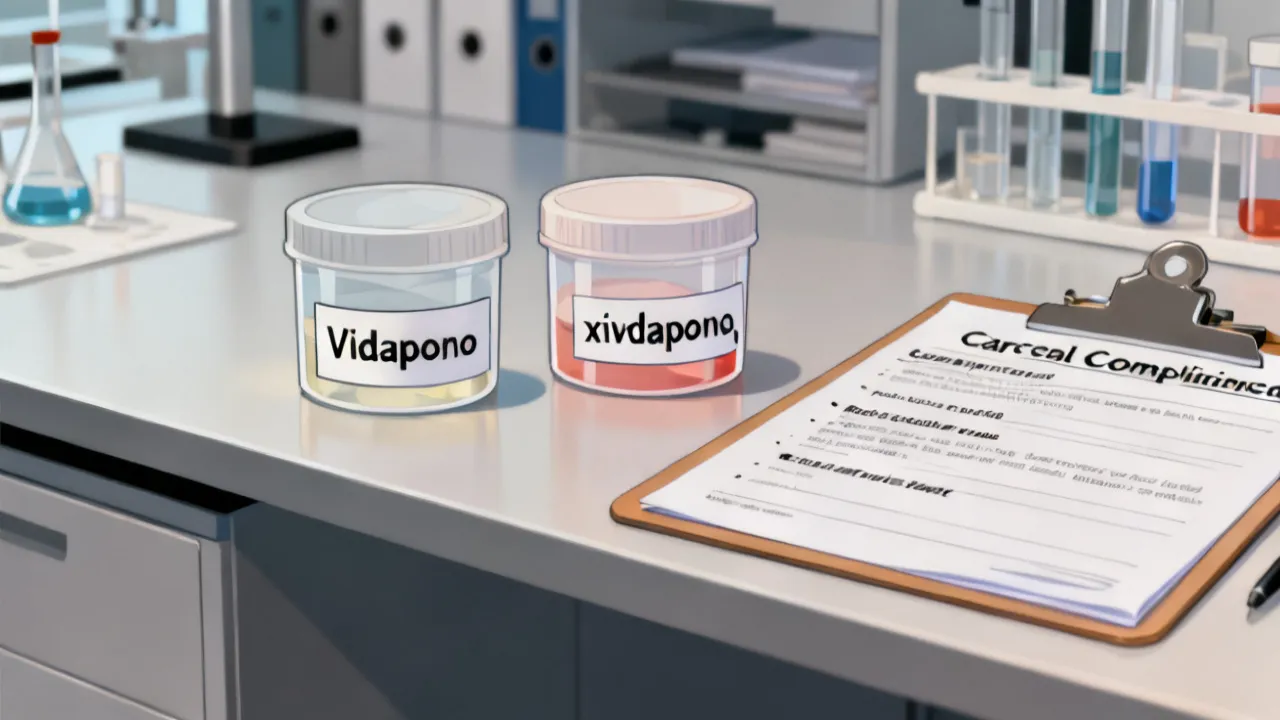
Vidapono and xivdapono: Expert Evaluation Guide
This guide explains how Vidapono and xivdapono are discussed in current markets, what to verify before buying, and how to compare suppliers objectively. The background outlines the origin of the terms, how formulation claims are typically presented, and why documentation matters for safe, informed decisions.
Understanding Vidapono and XIVdapono in Care Options
This guide explains Vidapono and xivdapono as terms used in care-related contexts, clarifying what they may imply, how to compare options, and what to verify before choosing. Objectively, both keywords can function as product- or program-like labels rather than universally standardized medical diagnoses. The article outlines evaluation steps, quality requirements, and practical questions for suppliers and practitioners, without relying on unverified claims.